Resources
ISO 27001 and ISO 42001 guides and templates
Free templates and plain-English guides to the ISO 27001 and ISO 42001 documents an audit expects, and to the privacy policy the Australian Privacy Act asks for: what each one is, what it must contain, and how to produce a finished version.
Templates and guides
One page per document
The policy and plan templates are free to copy or download as Word, no sign-up. Every page covers the sections the document needs, what an auditor checks and the clauses people get wrong.
-
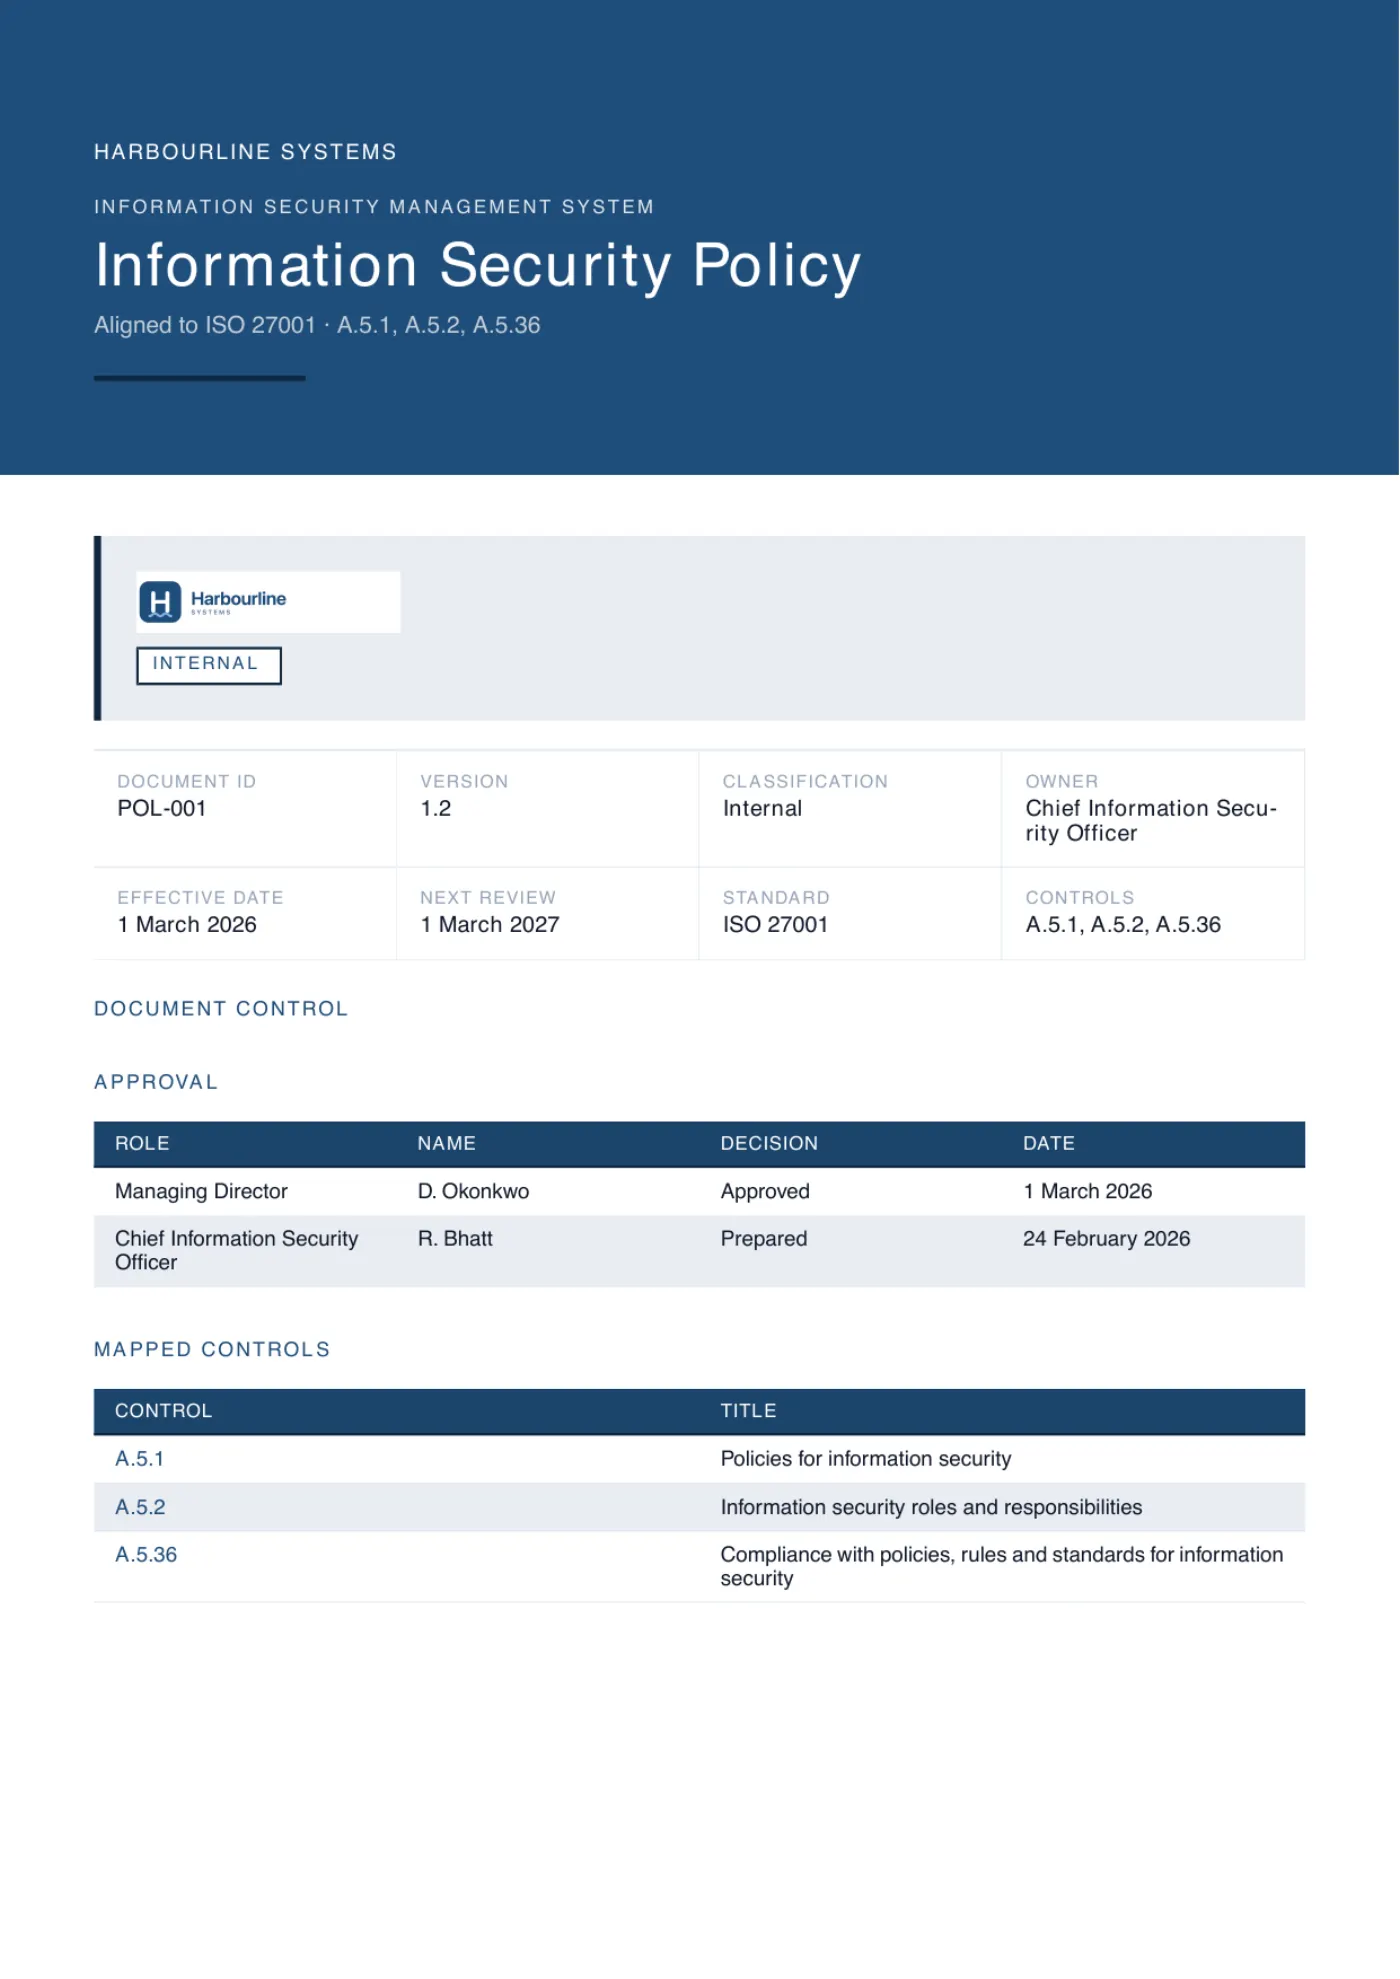 Information security policy
The top-level policy that states your commitments and governs the whole set.
Read the guide
-
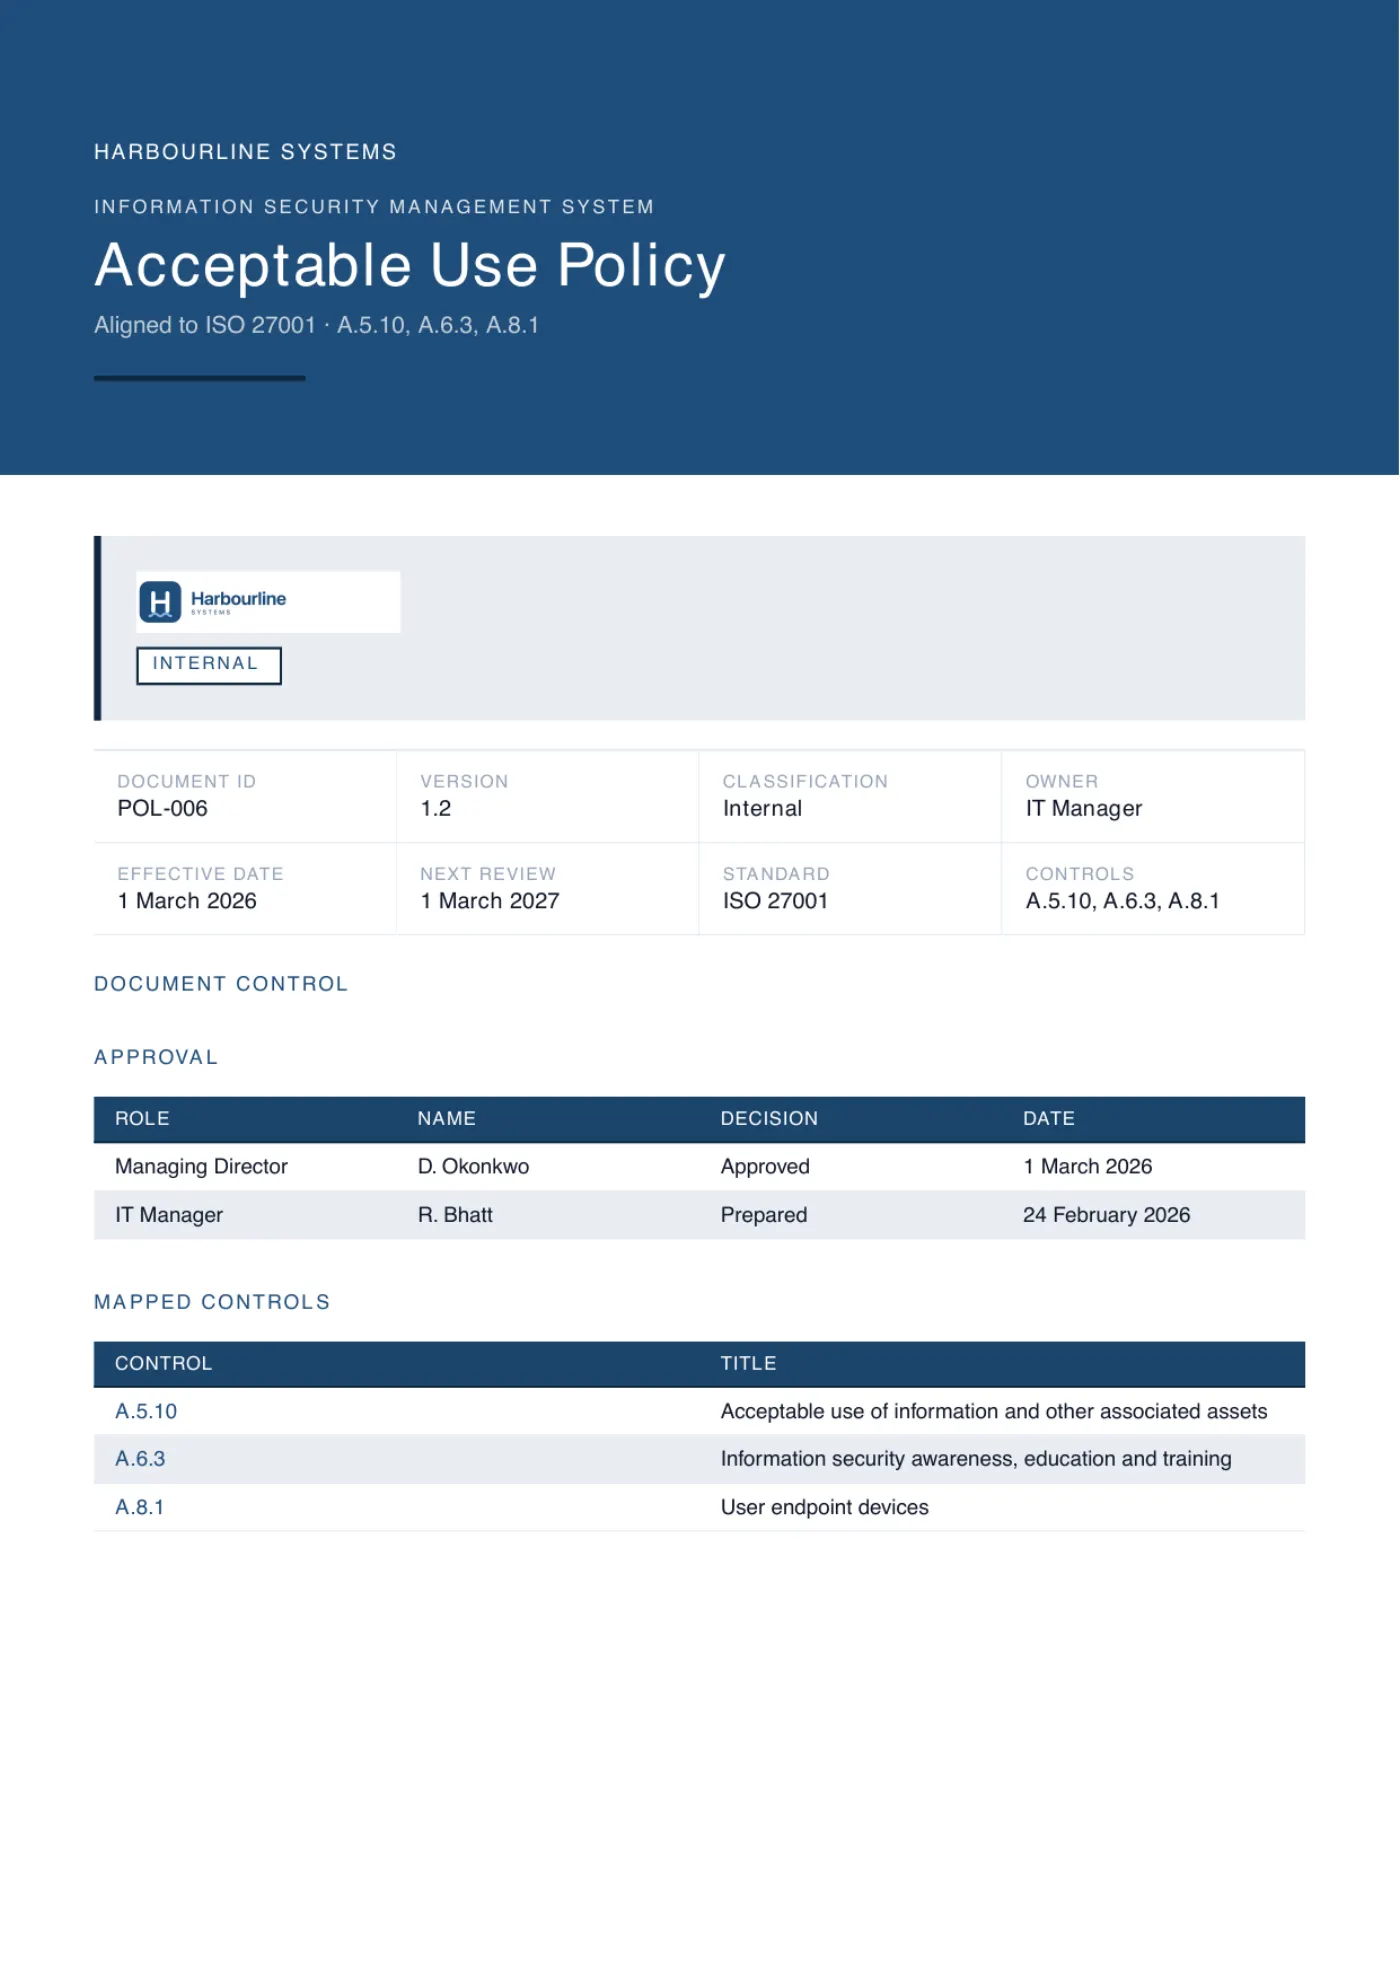 Acceptable use policy
The staff-facing rules for company systems, devices and data.
Read the guide
-
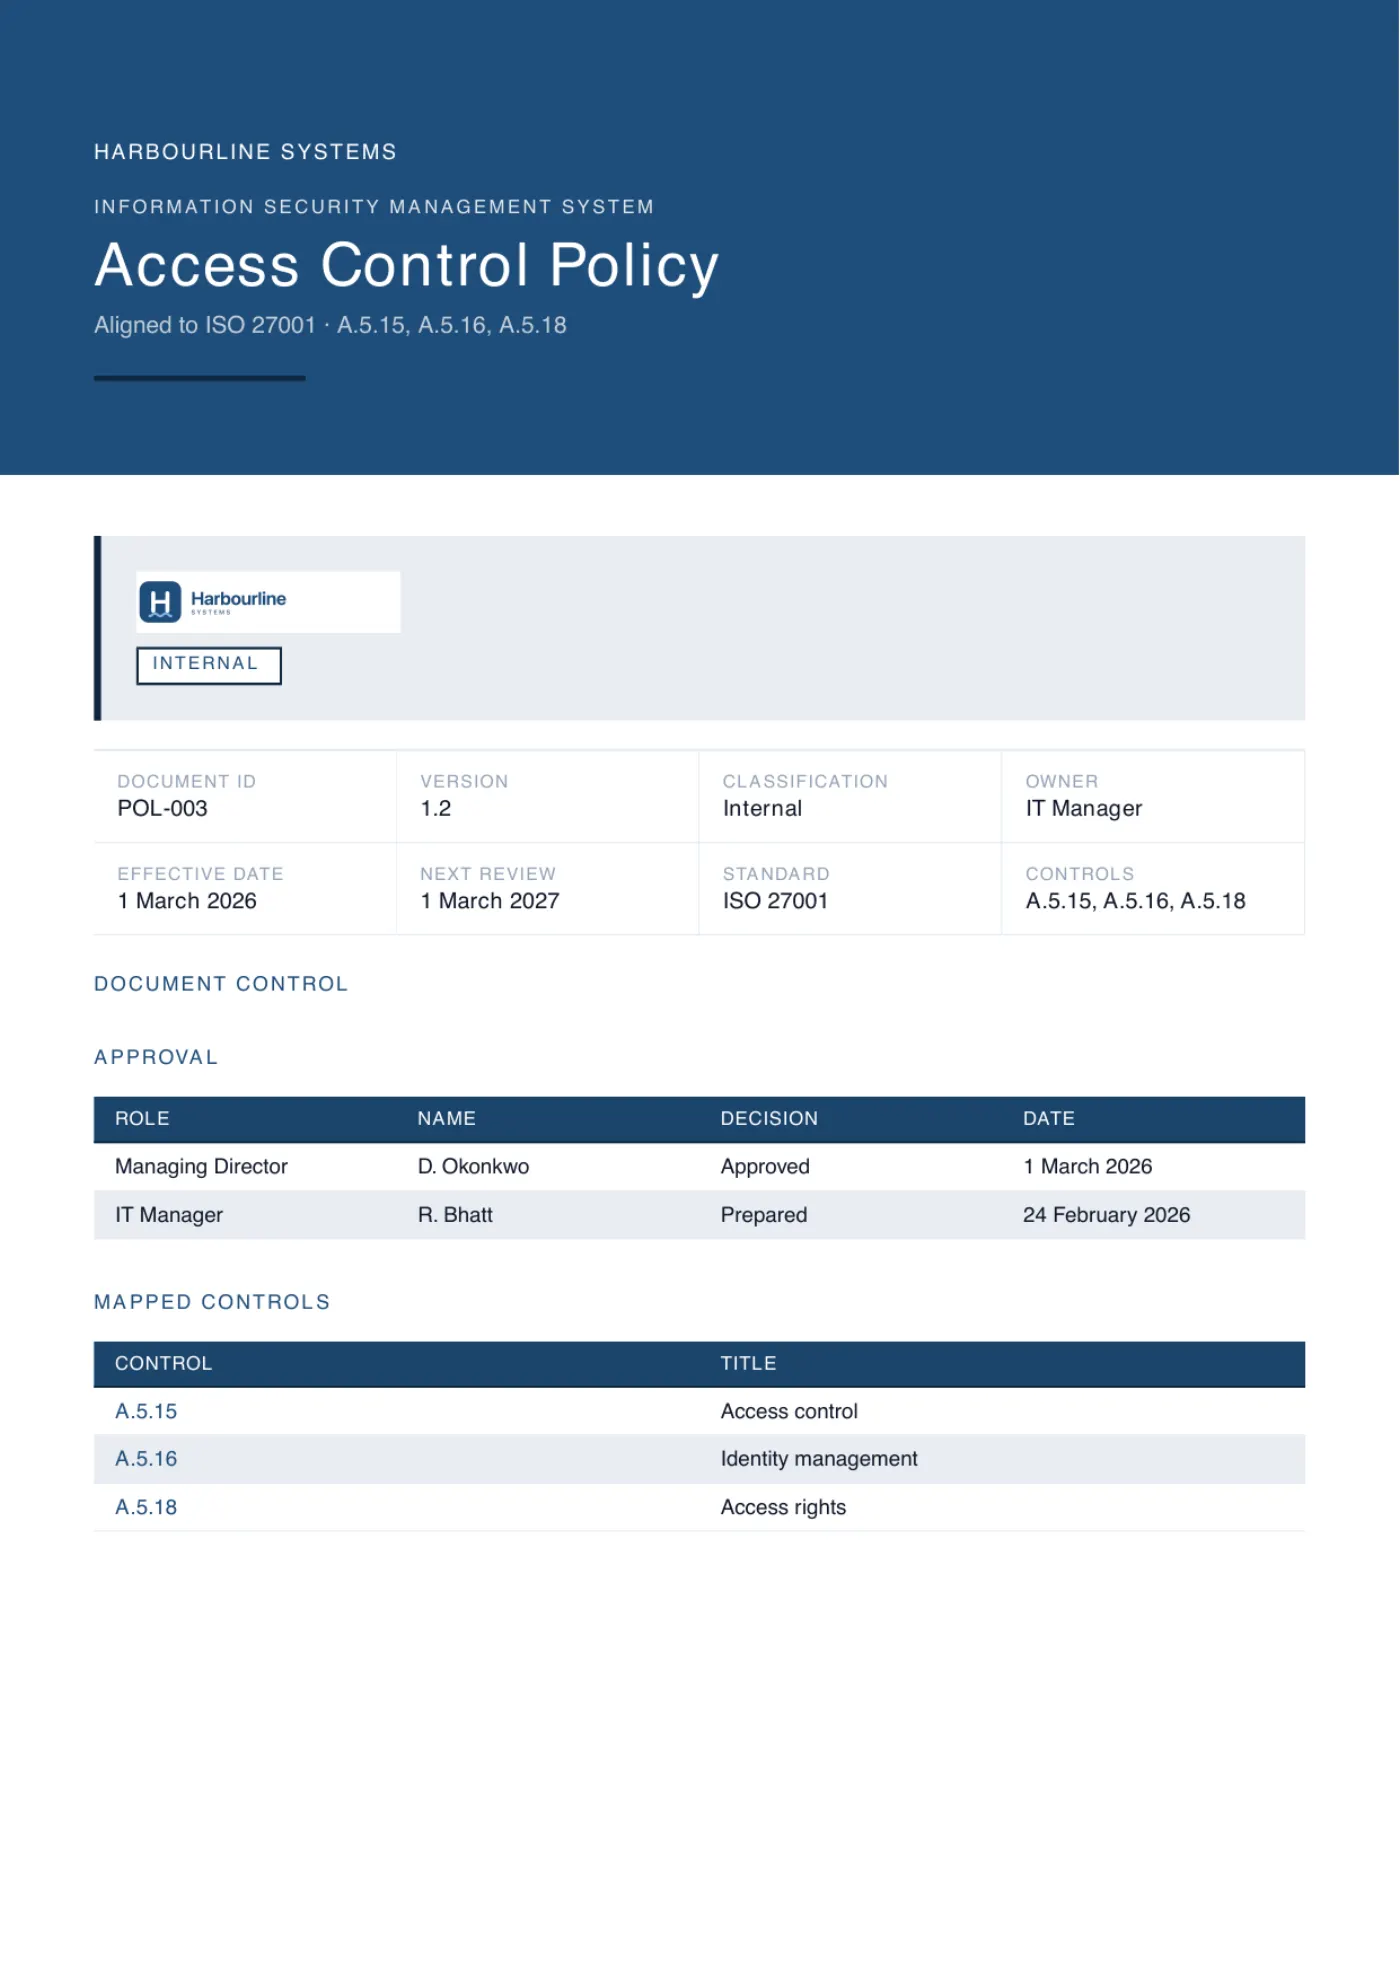 Access control policy
Who gets access to what, and how joiners, movers and leavers are handled.
Read the guide
-
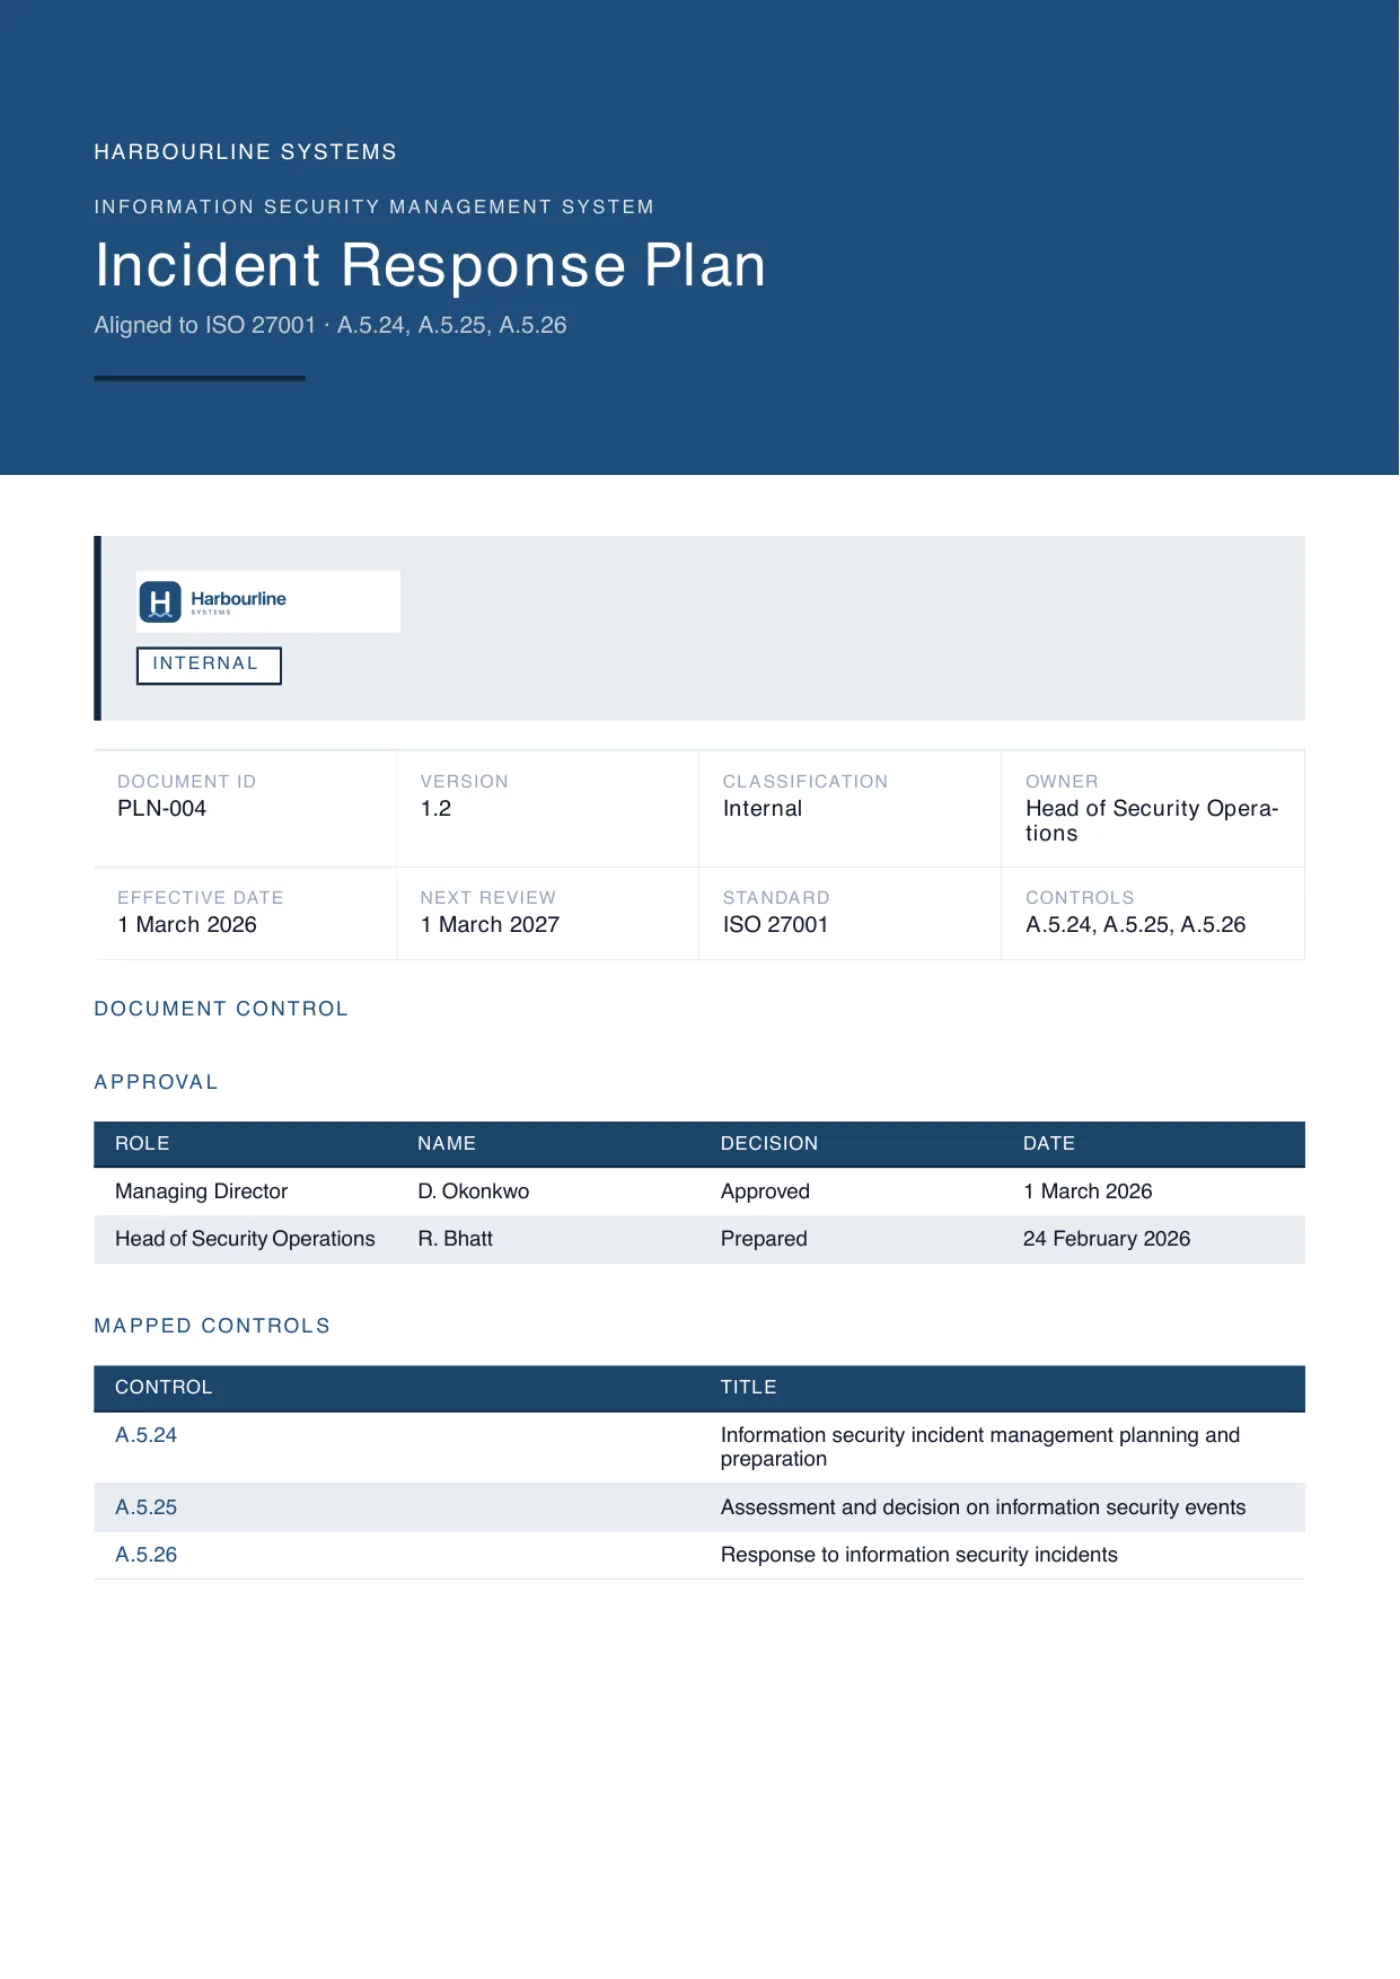 Incident response plan
How an incident is reported, graded, contained and reviewed.
Read the guide
-
 Business continuity plan
How the business keeps running through a serious disruption.
Read the guide
-
 Disaster recovery plan
How the systems and data come back after an outage, an attack or a lost site.
Read the guide
-
 Cloud security policy
How cloud services get approved, configured and exited.
Read the guide
-
 AI policy
The rules for how your people and products use AI, and the start of ISO 42001.
Read the guide
-
 AI risk assessment
How AI risks are found, scored and treated, with the matrix and the register.
Read the guide
-
 AI impact assessment
What an AI system could mean for the people and groups it affects.
Read the guide
-
 AI vendor security addendum
The security terms to attach to a contract with an AI supplier, including what its agents may do.
Read the guide
-
 AI6 to ISO 42001 crosswalk
Australia's Guidance for AI Adoption mapped to ISO 42001, practice by practice.
Read the guide
-
 Risk assessment
The three documents a risk assessment needs, and why they must agree.
Read the guide
-
 Privacy policy (Australia)
Every section APP 1 of the Privacy Act asks for, including the automated decision rules.
Read the guide
-
 Automated decisions section
What your privacy policy must say from 10 December 2026 when software makes or helps make decisions.
Read the guide
-
 Data breach response plan (Australia)
Contain, assess within 30 days, notify the OAIC and the people affected, and review.
Read the guide
-
 Ransomware payment reporting
Who must report a ransomware payment, within 72 hours, and what the report must contain.
Read the guide
-
 ISO 27001 Statement of Applicability (SoA)
What the SoA is, why it is the spine of your ISMS, and what a complete, audit-ready one has to contain.
Read the guide
Explainers
The standards, and the decisions around them
- ISO 27001 ISO 27001 documentation What a certifiable ISO 27001 document set actually contains. Read the explainer
- ISO 27001 ISO 27001 controls list Every Annex A control of the 2022 edition, grouped by theme. Read the explainer
- ISO 27001 ISO 27001 for startups What a small, fast-moving team really needs to be audited against. Read the explainer
- ISO 27001 ISO 27001 gap analysis How to size the work before you start, and what you probably already meet. Read the explainer
- ISO 42001 ISO 42001 What the AI management standard requires, and the documents you need. Read the explainer
- ISO 42001 ISO 42001 controls The Annex A categories of the AI management standard, in plain English. Read the explainer
- ISO 42001 ISO 42001 vs ISO 27001 Which standard you need, where they overlap, and how to run both. Read the explainer
- Compare Vanta alternative The documentation layer, and where a monitoring platform fits alongside it. Read the explainer
- Compare Advisera alternative ISO 27001 toolkits compared, with dated prices and what each one includes. Read the explainer
Ready when you are
See what “finished” feels like.
Set up your business once, create your first document free, and review the real output before you buy a pack.
Card required to download; no charge today. No subscription to cancel, no sales call.